Cybersecurity – cost or investment?
The cost of cybersecurity is a fundamental budget line item for any enterprise-scale organization. It is not a one-off purchse, but an ongoing operational commitment that includes software licensing fees, system implementation, infrastructure maintenance, specialized personnel costs, and incident response readiness. Consequently, an accurate budget estimation begins by identifying what the organization needs to protect and establishing the business downtine costs it aims to prevent.
Cybersecurity podcast
– Good morning, I’d like to purchase an XDR solution.
– Certainly, but what specific operational problem are we trying to solve?
This brief exchange illustrates a widespread challenge in security procurement, a primary topic explored in a recent cybersecurity podcast episode hosted by Perceptus. Organizations frequently request specific technology suites without defining the post-implementation outcomes they expect to achieve. Yet, answering that fundamental question dictates both the technical solution selection and the overall return on investment.
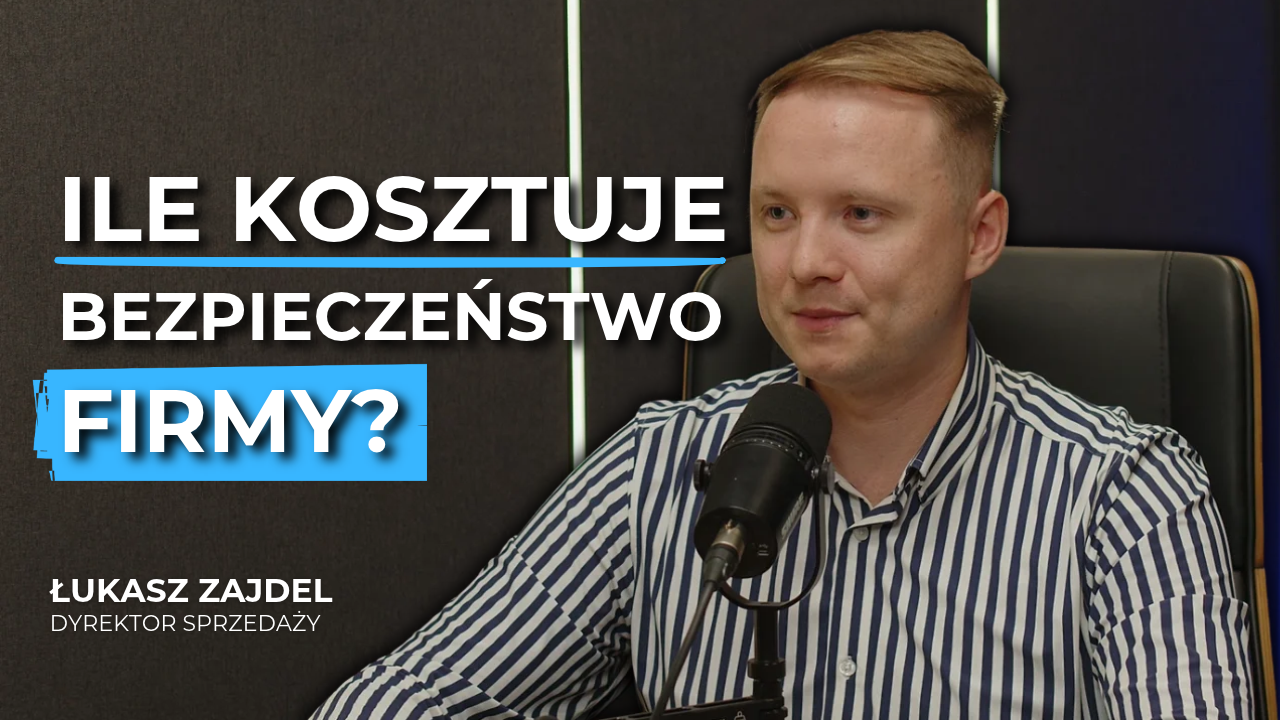
In this episode, Grzegorz Gąsiewski, Director of the SOC Department and Łukasz Zajdel, Sales Director at Perceptus discuss security budgets, procurement decisions, and vendor collaboration. Based on their field experience, conversations surrounding security investments must align directly with the organization’s daily operational workflows.
How much does cybersecurity cost, and how should a company plan its budget?
Evaluating an enterprise’s overall security posture based on a single software license is impossible. Comprehensive defense may require email and network protection, identity and access management (IAM), automated backup systems, employee security awareness training, as well as continuous monitoring and incident handling.
The required scope depends directly on infrastructure complexity and threat profile. Even organizations with identical employee headcounts can present drastically different requirements – for instance, a fully cloud-native enterprise versus an industrial manufacturer operating production plants across multiple sites.
When planning cybersecurity investments, organizations should account for the following core budget categories:
| Budget component | Key items to include |
|---|---|
| State assessment & roadmap | Asset inventory, security audits, risk analysis, and priority setting |
| Technologies | Licenses, recurring subscriptions, hardware, and supporting operational infrastructure |
| Implementation | Security configuration, cross-platform integrations, data migration, testing, and admin knowledge transfer |
| Maintenance & operations | Patch updates, event analysis, detection rule tuning, internal IT hours, or external managed services |
| Verification & evolution | Data recovery testing, incident response drills, staff training, and adapting to organizational changes |
A baseline budget must cover both initial deployment and ongoing lifecycle operations. When evaluating vendor proposals, comparing costs over a standarized multi-year timeframe (e.g., three years) reveals the true total cost of ownership (TCO), accounting for renewal spikes, operational management, and infrastructure expansion.
Selecting technology matched to organizational needs
Deploying an XDR (Extended Detection and Response) framework is justified when an enterprise needs enhanced visibility to detect suspicious activity and correlate complex event streams. However, XDR alone will not resolve underlying challenges in access control, disaster recovery, or operational policy enforcement. Similarly, deploying a next-generation firewall requires network-tailored configuration and ongoing administration.
Instead of initiating procurement with a product brand, organizations should define the intended outcome: accelerating compromise detection on privileged accounts, enforcing least-privilege access to legacy ERP systems, or restoring critical services within business-defined Recovery Time Objectives (RTO).
Once formulated, these operational objectives can be tested during project execution. Teams can verify whether monitoring covers designated assets, alerts route to appropriate responders, and recovery drills meet targeted recovery windows. Purchasing a license alone provides no answer to these core operational criteria.
This outcome-driven approach also optimizes expenditure. A through audit often reveals that an organization already owns necessary security features within existing platforms that remain unconfigured or underutilized. Prior to issuing new purchase orders, organizations should evaluate the full capabilities of their current tech stack and eliminate adoption bottlenecks.
How to discuss cybersecurity costs with the board?
As Grzegorz Gąsiewski notes in podcast, “cybersecurity is still predominantly viewed as a cost center”. This perspective is understandable from a financial approval standpoint: purchasing new manufacturing equipment directly scales production capacity, while hiring sales reps directly drives top-line revenue. By contrast, the ROI of cybersecurity controls is harder to quantify – especially if the organization has not yet experienced a major operational outage.
Justifying security investments requires framing them around core business processes.
- What is the immediate financial impact if access to the warehouse management system is lost?
- How long can customer orders be processed manually if email or SaaS platforms go offline?
- Which specific databases are essential to maintain production line continuity?
Estimating downtime costs under concrete operational scenarios provides financial clarity. Quantifying these variables allows leadership to evaluate the value of reducing Recovery Time Objectives. It does not mean every security expenditure yields a positive cash return; decision-making requires weighing threat probabilities against the degree to which proposed controls mitigate operational risk.
Real-world incident cost breakdown: The Marks & Spencer case
In its 2025/26 financial results, retail giant Marks & Spencer reported £131.3 million in direct expenses resulting from a major cyber incident. Of this sum, £109.3 million was attributed to incident response, system containment, and operational recovery, while £22 million went toward third-party forensic and advisory specialists. The company separately reported the net impact on retail trading along with insurance recoveries.
This enterprise case study demontrates why incident accounting must be broken down into discrete operational categories. Restoring compromised IT infrastructure represent only one portion of the bill. Business interruption, emergency staff utilization, legal compliance fees, and specialized external support make up the rest. While the scale of a global enterprise differs form mid-sized companies, adopting this cost-categorization model helps any organization prepare realistic risk evaluation.
Where to start cybersecurity investment planning
Phasing security investments distributes both financial commitments and operational workload across internal teams. Implementation roadmaps must balance threat urgency against statutory compliance deadlines.
When asked for a primary recommendation for organizations initiating security planning, Łukasz Zajdel emphasizes: “Firts and foremost, start with a comprehensive security audit.”
A well-defined audit scope determines current assets, exposes critical vulnerabilities, and prioritizes remediations. The output provides baseline for a structured roadmap detailing cost projections, clear ownership, execution timelines, and strategies to maximize existing toolsets.
When preparing a Request for Proposal (RFP), organizations should gather data on endpoint counts, physical and cloud locations, critical applications, existing security controls, required monitoring hours (e.g., 24/7 coverage), internal IT team capabilities, and acceptable Maximum Tolerable Downtime (MTD).
With these variables defined, asking “How much does cybersecurity cost?” yields comparable, competitive vendor proposals anchored in real business requirements. Leadership can evaluate the specific risk each budget line item mitigates, designate accountable personnel, and establish clear metrics to audit performace.
Planning a cybersecurity investment? Contact our team to schedule an IT Security Audit to prioritize your roadmap and define your project scope.
Looking to enhance your cybersecurity?
Contact us!
Leave your details – we’ll call you back
Our specialist will get back to you no later than the next business day. You don’t have to fill in the message field, but a brief note about the topic you’re interested in will be a valuable hint for us.